 Mauricio Cuello
Your security toolchain didn’t break. It just couldn’t keep up with the cloud. It’s been a while since I posted here, so let me start with what I’ve been heads-down on lately: evaluating two of the heaviest players in the CNAPP (Cloud-Native Application Protection Platform) space.
Before I share what I’m finding, let me explain why this category even exists — because it’s easy to dismiss CNAPPs as “yet another platform” until you’ve felt the problem yourself.
Cloud environments don’t grow linearly. They grow the way complexity does — slowly, then all at once. The moment scaling becomes a real need, containers, orchestrators, VMs, and serverless functions start spinning up fast. DevOps teams create and destroy resources with ease, and security configuration isn’t always the priority when shipping speed is the north star. That’s not a criticism — it’s the reality of how modern platforms operate.
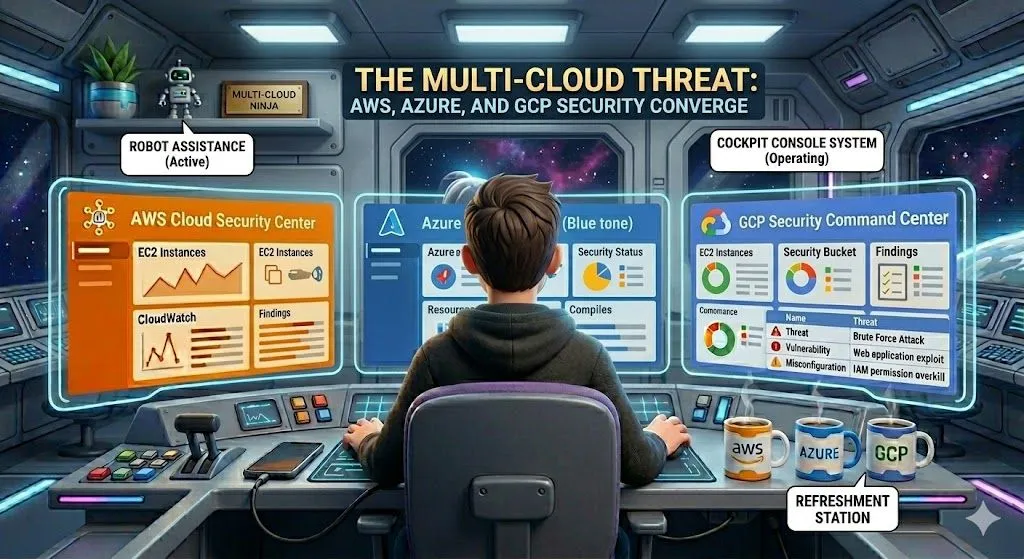
The problem lands on security teams. Let’s say you start on AWS. You enable AWS Security Hub to track misconfigurations. Solid. Then the product team decides to run something on Azure. Now you’re enabling Microsoft Defender for Cloud. Then someone spins up a GCP project. Add Google SecOps to the list.
Now you have three findings sources, three severity formats, three dashboards — and despite each provider’s honest efforts to be interoperable, there’s a significant amount of custom plumbing to do before you can see everything in one place. And that’s only the CSPM layer — just misconfigurations and compliance. Add CWPP (workload protection for your containers and VMs), CIEM (who actually has access to what and why), and DSPM (where your sensitive data lives and whether it’s exposed) — and the operational complexity doesn’t add up, it multiplies.
That’s the gap CNAPPs are designed to close. One onboarding process per data source. One unified asset inventory. One detection pipeline generating alerts across all capabilities, across all clouds. Whether that promise holds up in practice — and at what cost — is exactly what I’m in the middle of figuring out. When your environment grew past a single cloud provider, how did you handle the security visibility problem — native tools, a CNAPP, or something else entirely?
More on what I’m finding soon.
 Mauricio Cuello